
The Problem
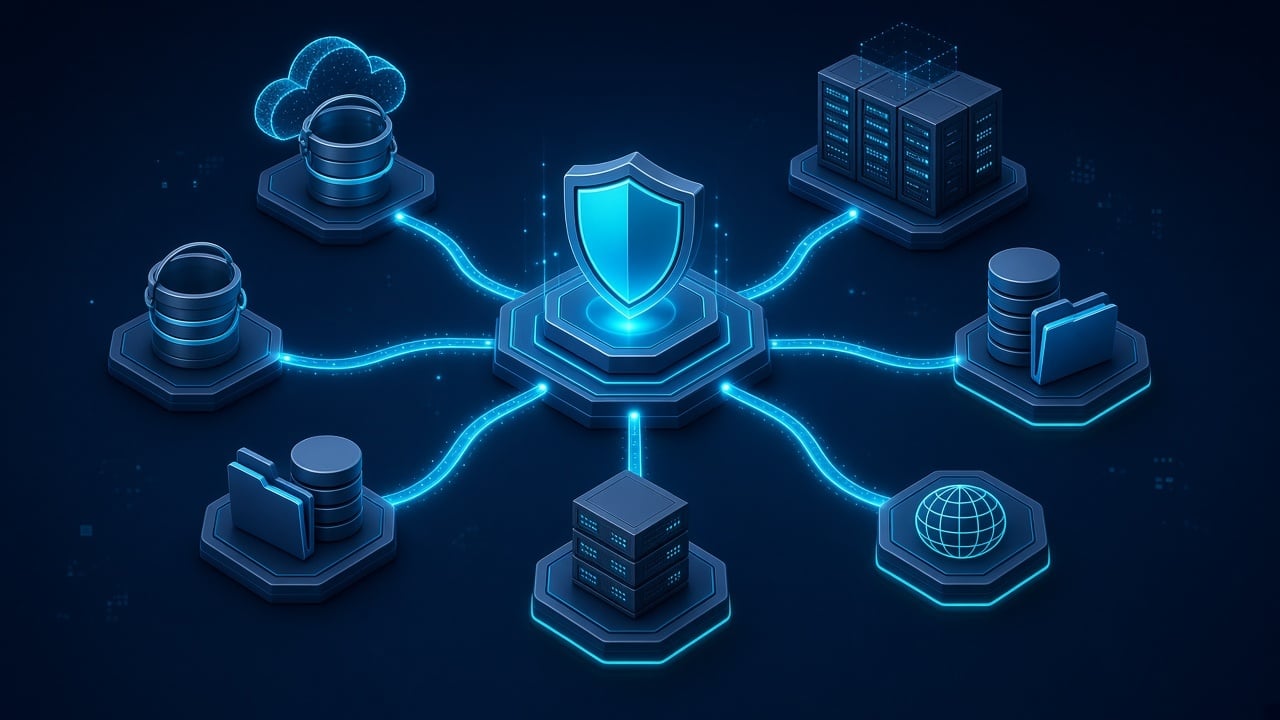
AI models and agents are only as useful as the data they can reach. In most enterprises that data is spread across many systems: object storage in several clouds, on-premises file shares, and internal APIs.
Connecting to all of them usually means storing long-lived keys and passwords. Those standing credentials are exactly what privileged access management (PAM) and zero-trust programs try to eliminate. Every static secret is one more thing that can leak, be over-used, or be forgotten.
The Solution: Broader Reach, Just-in-Time Access
The latest ShardSecure MCP capabilities address both sides of the problem:
- New data source drivers let MCP retrieve data from far more of the places it actually lives.
- Credential providers let those drivers obtain short-lived credentials at the moment of access, instead of relying on standing static keys.
New Data Source Drivers
In addition to ShardSecure Secure S3, AWS S3, Google Drive, and Microsoft SharePoint, ShardSecure MCP now supports:
- Azure Blob Storage
- IBM Cloud Object Storage
- Oracle Cloud Object Storage
- Generic S3-compatible storage
- SMB file shares
- NFS file shares
- REST APIs
The S3-family drivers share a common architecture, so behavior is consistent across providers and each vendor needs only its specific differences. All drivers are managed from the ShardSecure Admin UI, with dedicated configuration forms for each data source type. Support for database sources and custom drivers is upcoming.
Credential Providers: Short-Lived Access Instead of Standing Secrets
Drivers no longer need to hold permanent secrets. Instead, a driver asks a credential provider for valid credentials for its data source and receives them with an expiry. Credentials are renewed before they expire and returned or revoked when no longer needed. The driver never needs to know where the credentials came from.
The framework is vendor-neutral. The first integrations are:
- HashiCorp Vault — KV v2 secrets and dynamic AWS and database credentials, with lease renewal and revocation.
- Delinea Secret Server — secret retrieval with check-out and check-in.
Static credentials remain supported for environments that need them. Credential providers are configured centrally in the Admin UI and can be reused across data sources, and the framework is designed to be extended to additional providers in the future.
How It Works
- An administrator configures a credential provider, such as Vault or Delinea, in the Admin UI.
- Each data source is set to use either static credentials or a configured provider.
- When an AI agent request reaches ShardSecure MCP, the driver obtains short-lived credentials from the provider at the moment of access.
- MCP applies identity-aware policies and dynamic redaction, and retrieves only the allowed data.
- Credentials expire, are renewed, or are returned—no standing secret remains in the driver.
Key Benefits
- Wider coverage — Reach data across multiple clouds, on-premises file shares, and APIs from one MCP server.
- No standing credentials — Access is granted just in time and expires automatically.
- Fits your PAM strategy — Works with existing secrets and privileged access platforms rather than replacing them.
- Vendor-neutral — One framework, multiple providers, with room to grow.
- Complements proxy-based approaches — Works alongside PAM proxies such as StrongDM, which check privileged actions in real time.
- Central management — Data sources and credential providers are configured in the Admin UI.
Why This Matters
As AI agents take on more autonomous work, the systems that feed them data become privileged components in their own right. Extending ShardSecure MCP to more data sources while removing standing credentials brings zero-trust principles all the way down to the connection between MCP and your data.
Evaluation / POC
ShardSecure MCP is available for no-cost evaluation by enterprise customers and partners. Contact us at info@shardsecure.com to schedule a technical briefing or proof-of-concept.
Ready to extend secure AI access across your data sources?
Contact info@shardsecure.com for a no-cost evaluation.